

Oct 27, 2026
Save for later
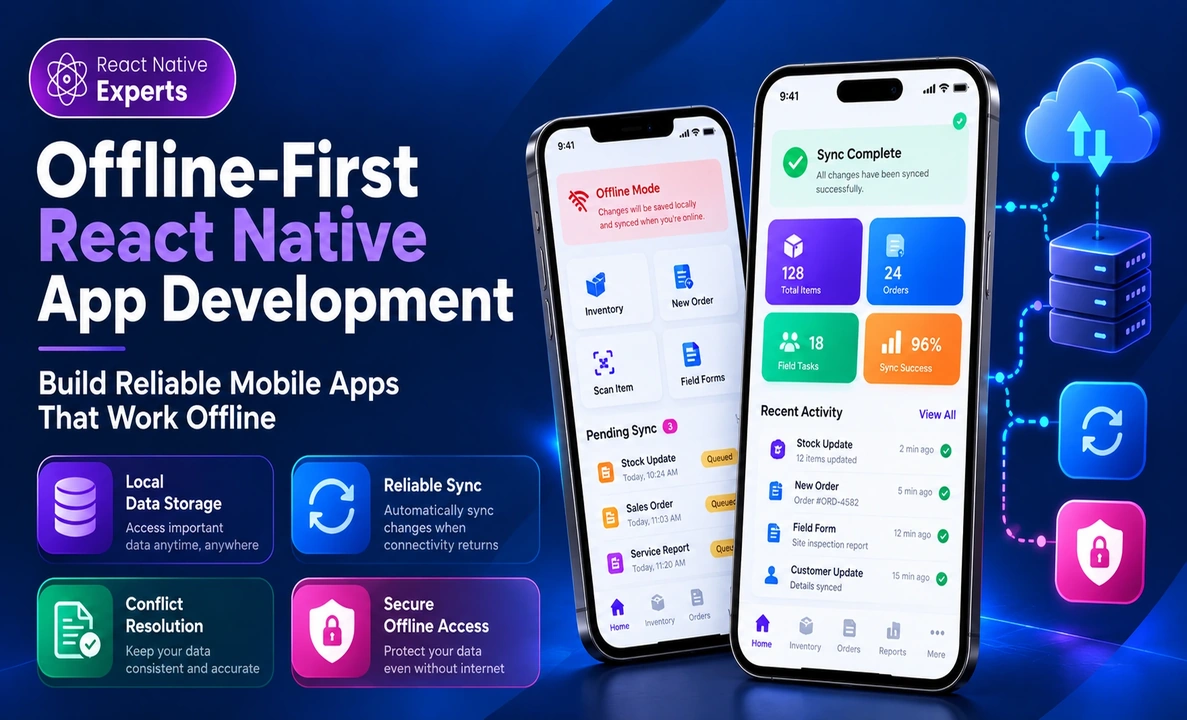
Introduction A mobile app should not stop working simply because the internet connection drops. For businesses operating in warehouses, remote locations, delivery routes, or areas with unreliable network coverage, offline functionality can be essential to daily operations. Offline-first React Native app development helps businesses build applications that continue performing important tasks without a constant internet […]
 React native Experts
Introduction Building a mobile app is more than writing code and publishing it to the App Store or Google Play. A successful application needs a clear purpose, intuitive user experience, reliable technology, thorough testing, and a plan for what happens after launch. Whether you are developing a startup MVP, a business application, an eCommerce app, […]
React native Experts

Introduction Businesses are increasingly using mobile apps to make their services more accessible, improve customer engagement, streamline internal operations, and create new revenue opportunities. From customer-facing apps and employee platforms to booking systems, marketplaces, and enterprise solutions, mobile applications have become an important part of modern business strategies. However, building a business app requires more […]
React native Experts
Introduction: Businesses increasingly need applications that can handle changing traffic, connect with multiple services, support distributed teams, and evolve without requiring a complete rebuild. Traditional application architectures can struggle when growth introduces more users, integrations, data, and operational complexity. Cloud app development services provide an approach to building applications around cloud infrastructure, managed services, APIs, […]
React native Experts
Introduction: React Native Paper is a popular UI framework that makes it simple for developers to design user interfaces that are highly dynamic, visually beautiful, and consistent. It provides an extensive collection of pre-designed elements, such as buttons, cards, dialogs, and more, and is based on Google’s Material Design principles. This enables developers to concentrate […]
React native Experts
Introduction A mobile app does not become outdated overnight. It usually happens gradually. Performance starts declining. Users report bugs more often. Dependencies become difficult to update. New features take longer to develop. The interface begins to feel behind competing applications. Eventually, even small changes require more development effort than they should. For businesses with an […]
React native Experts
Introduction Subscriptions have become a popular way for mobile businesses to generate recurring revenue. Fitness platforms, eLearning apps, productivity tools, streaming services, SaaS products, and premium-content applications can all benefit from this model. But building a subscription app involves more than adding a payment button. The application needs to handle plans, purchases, renewals, cancellations, failed […]
React native Experts
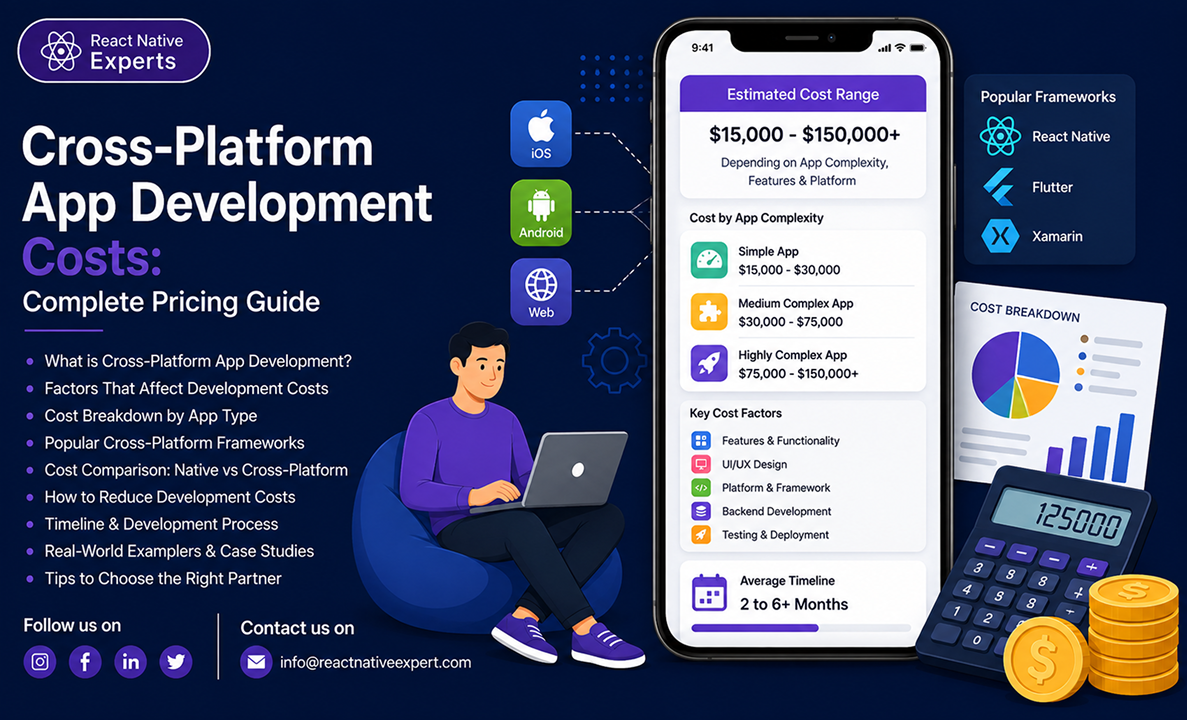
Cross-Platform App Development Costs Guide The cost of cross-platform app development in 2026 can range from a relatively modest budget for a simple MVP to a much larger investment for a complex application with real-time features, payments, AI, advanced security, and custom backend infrastructure. There is no single price that applies to every project. The […]
React native Experts
Marketplace App Development Company Launching a marketplace sounds straightforward: bring buyers and sellers together in one app. In reality, a successful marketplace needs much more than product listings. Buyers need a simple way to discover and purchase products or services. Sellers need tools to manage listings and orders. Meanwhile, the business behind the platform needs […]
React native Experts
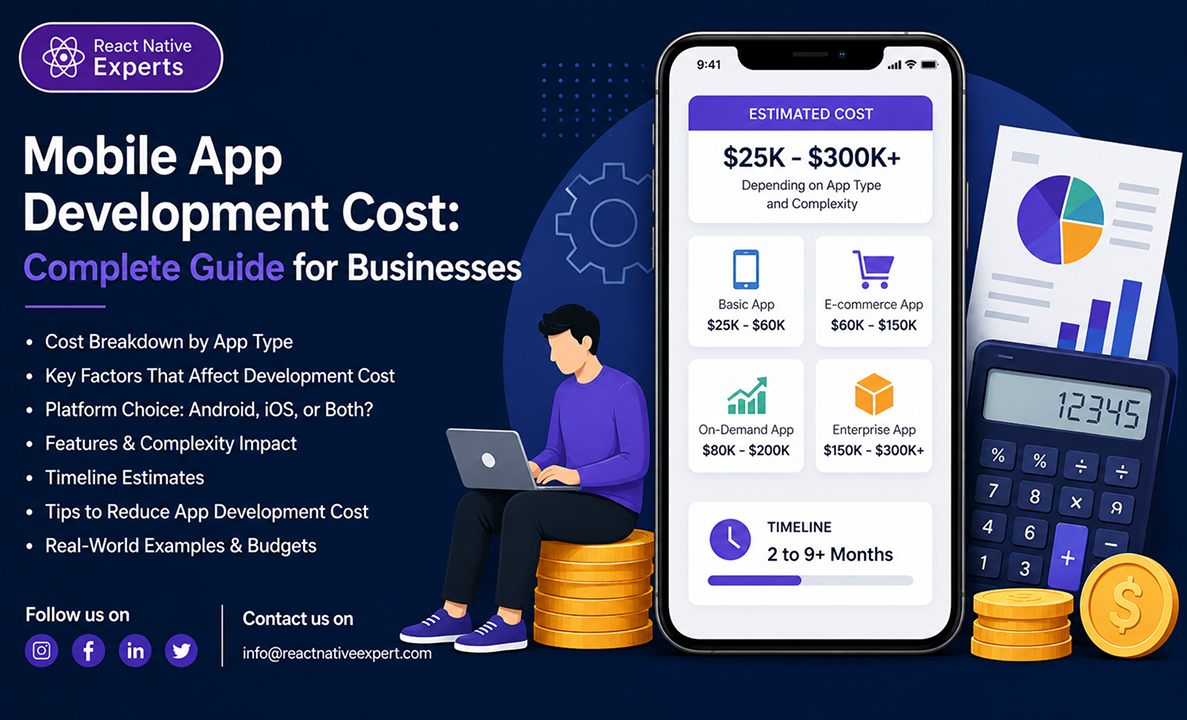
Introduction: If you’ve started researching mobile app development, you’ve probably noticed that cost estimates can be all over the place. One company might quote a few thousand dollars. Another might give you a six-figure estimate. Then you come across an article claiming that an app can be built in a few weeks. So, what does […]
React native Experts
Introduction: Not every mobile app is built to entertain users or sell products. Sometimes, the simplest utilities become the most frequently used applications. A digital ruler is a great example. Whether someone needs to measure a package, check the dimensions of a piece of furniture, estimate the size of a document, or assist with DIY […]
React native Experts
Introduction: Inventory is one of the most valuable assets a business owns. Whether you’re running an online store, managing multiple warehouses, operating a manufacturing facility, or supplying products across different locations, knowing exactly what you have in stock can make the difference between smooth operations and costly mistakes. We’ve spoken with businesses that still rely […]
React native Experts
Introduction The way people access pharmacy services is changing. Customers increasingly expect convenient ways to find medicines, submit prescriptions, check order status, and manage repeat purchases through digital platforms. For pharmacies and healthcare businesses, a well-planned mobile application can support these expectations while making everyday operations easier to manage. However, building a successful pharmacy application […]
React native Experts

Introduction Mobile applications handle an increasing amount of personal, business, and financial information. From customer accounts and payment details to location data and confidential business records, the information stored and transmitted by an application needs appropriate protection. As mobile threats evolve, security must be considered throughout the development lifecycle rather than added just before launch. […]
React native Experts
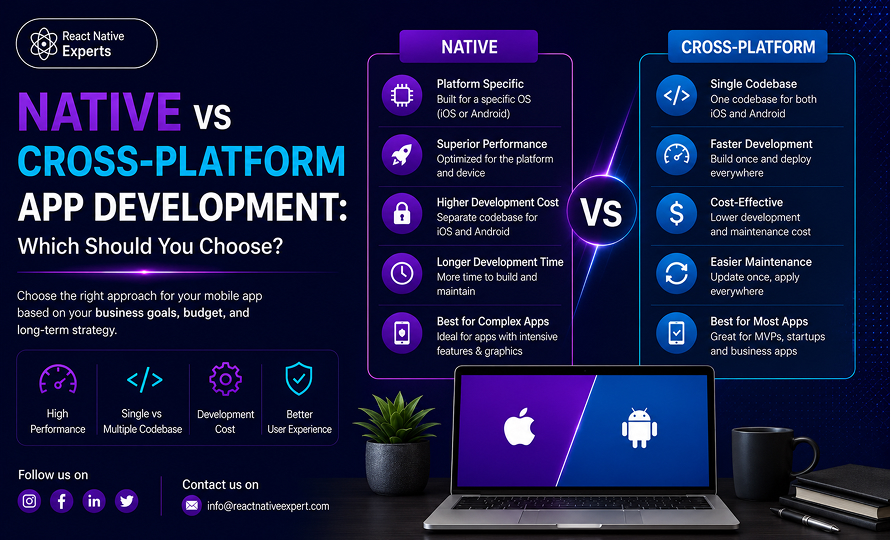
Introduction Choosing between native and cross-platform app development is one of the first technical decisions businesses face when planning a mobile product. The choice affects development cost, launch timelines, maintenance, performance, access to native features, and how easily the application can evolve. In 2026, the decision is less about whether one approach is universally better. […]
React native Experts
Expo vs React Native: Understanding the Best Choice for Your Mobile App Expo and React Native are often discussed together because both are used to build mobile applications with JavaScript or TypeScript. However, they are not exactly competing technologies. React Native is the underlying framework for building native mobile applications, while Expo provides a development […]
React native Experts

Introduction: The courier and logistics industry is increasingly dependent on digital platforms to manage orders, drivers, customers, payments, tracking, and delivery operations. Customers expect convenient booking, accurate tracking, quick communication, and reliable delivery updates, while courier businesses need better tools to coordinate drivers and shipments. A modern courier delivery app needs to do more than […]
React native Experts
Introduction: The salon industry has become more digital than ever. Today’s customers expect to book appointments, receive reminders, make payments, and manage their salon visits directly from their phones. If a salon still relies on manual scheduling and phone calls, it risks losing customers to competitors that offer a more convenient experience. This is why […]
React native Experts
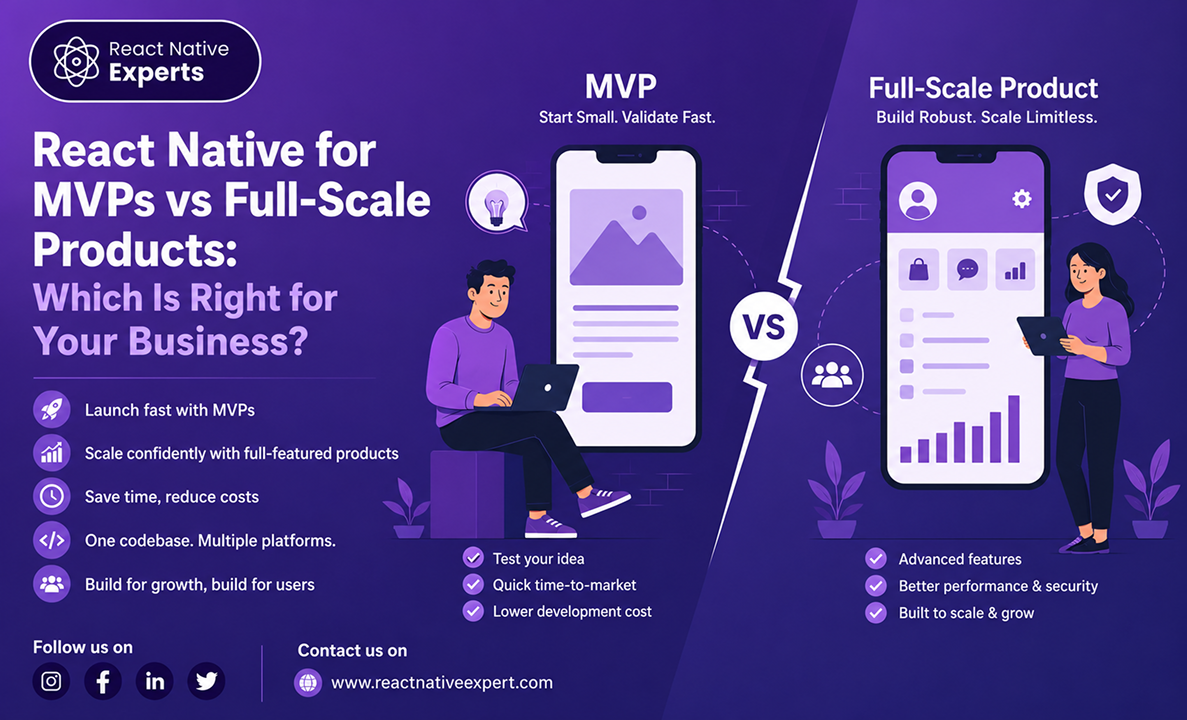
Introduction: When planning a mobile application, one of the most important decisions a business must make is whether to start with a Minimum Viable Product (MVP) or invest directly in a full-scale product. The choice affects everything from development costs and timelines to scalability and long-term growth. Many startups assume they need a simple MVP […]
React native Experts
Introduction: Choosing the right development team is one of the most important decisions when planning a React Native mobile application. Businesses need to consider more than the technology itself. They also need to decide who will build the product, how the team will be managed, how development costs will be controlled, and what level of […]
React native Experts
Introduction: When planning an iOS mobile application, one of the first technical decisions businesses face is choosing the right development approach. Two of the most popular options are React Native and Swift. Swift is Apple’s native programming language for iOS app development, while React Native is a cross-platform framework developed by Meta that allows developers […]
React native Experts
Introduction: Telemedicine has changed how patients connect with healthcare providers by making consultations and healthcare services accessible through digital platforms. A well-designed telemedicine app can allow patients to find doctors, book appointments, attend video consultations, exchange messages, access medical information, receive prescriptions where supported, and manage follow-up care from a mobile device. For healthcare businesses, […]
React native Experts
Introduction: Most travelers no longer call hotels to make reservations. They compare prices, check reviews, browse rooms, make payments, and manage bookings directly from their phones. If your hotel business does not offer a smooth mobile experience, users move to platforms that do. That is why hotel booking app development is becoming essential for hotels, […]
React native Experts

Introduction: Software as a Service (SaaS) businesses increasingly need mobile applications that let customers access their accounts, manage subscriptions, collaborate with teams, and complete important tasks from anywhere. A well-designed SaaS mobile app can make a product more accessible, improve the customer experience, and create additional opportunities for engagement and retention. React Native is one […]
React native Experts
Why Businesses Are Switching to React Native for App Development Mobile app development has become a critical part of digital transformation, but building separate apps for Android and iOS can be expensive and time-consuming. This is why many companies are now switching to React Native as their preferred framework. React Native allows businesses to build […]
React native Experts
Introduction Choosing the right technology for a mobile app can have a direct impact on development time, maintenance costs, scalability, and the overall user experience. For businesses planning to launch applications on both iOS and Android, React Native is one of the technologies worth considering. React Native allows development teams to build mobile applications using […]
React native Experts
Introduction: Buy Now Pay Later (BNPL) has become an important payment option for businesses that want to give customers more flexibility at checkout. Instead of paying the entire purchase amount upfront, eligible customers can split the cost into scheduled installments under agreed repayment terms. For fintech startups, retailers, lenders, and e-commerce businesses, launching a BNPL […]
React native Experts
Introduction: Healthcare is becoming increasingly connected. Patients can book appointments from their phones, attend virtual consultations, receive medication reminders, track health information, and communicate with healthcare providers without always needing to visit a clinic. For healthcare businesses, this creates an opportunity to make services more accessible through well-designed digital health applications. But healthcare apps aren’t […]
React native Experts
Introduction: Launching a startup often means making difficult decisions about where to invest limited time and resources. Mobile app development is one of the biggest investments many startups make, and choosing the right technology stack can significantly affect costs, development speed, and future scalability. This is why React Native apps for startups have become increasingly […]
React native Experts
Introduction: Mobile app development continues to evolve rapidly, and React Native remains at the forefront of this transformation. Businesses are increasingly adopting React Native to build scalable, high-performance applications while reducing development time and costs. As competition grows, staying updated with the latest React Native trends is essential for building future-ready applications that deliver strong […]
React native Experts
Introduction: The food delivery industry has seen massive growth in recent years, driven by changing consumer habits and the demand for convenience. Platforms like Zomato and Uber Eats have completely transformed how people discover and order food. For businesses, this presents a strong opportunity. Investing in food ordering app development allows you to build a […]
React native Experts
Introduction: Real estate mobile applications have become essential tools for property agencies, brokers, developers, and real estate marketplaces. Today’s buyers and renters expect to browse listings, view property photos, schedule visits, communicate with agents, and receive property updates directly from their smartphones. As demand for digital property experiences continues growing, many businesses ask the same […]
React native Experts
Introduction: Renting a car today is very different from what it was a few years ago. Customers no longer want to visit a rental office, fill out paperwork, or wait in line to collect a vehicle. They expect to browse available cars, compare prices, upload their driving licence, make secure payments, and unlock their rental […]
React native Experts
Introduction: Manufacturing mobile app development is transforming how factories operate by enabling real-time visibility, automation, and data-driven decision-making. From production tracking to inventory management and workforce coordination, mobile apps help manufacturers streamline operations and improve efficiency. If you are dealing with delayed reports, manual tracking, miscommunication between teams, or lack of real-time visibility, you are […]
React native Experts
Introduction When drivers face a breakdown, flat tire, dead battery, or accident, speed matters. Most people do not want to search online, make multiple calls, or explain their location repeatedly during a stressful situation. They expect instant roadside assistance directly from their phone. That is why road assistant app development is growing rapidly across towing […]
React native Experts
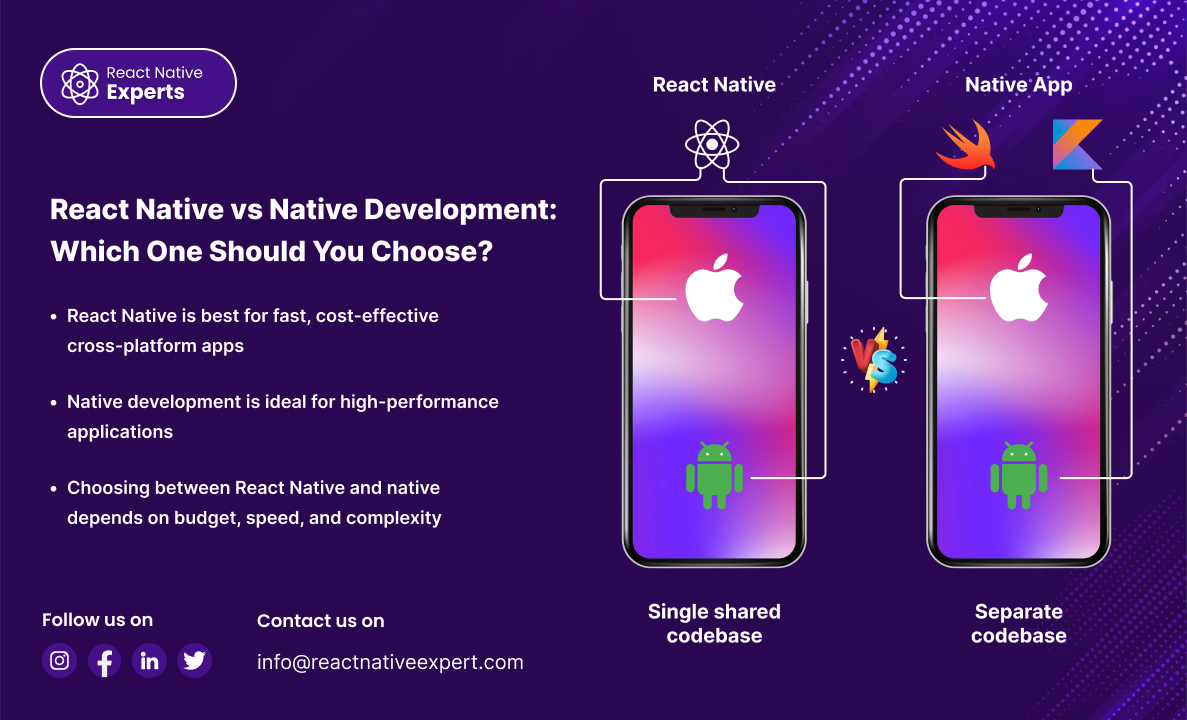
Introduction: Choosing between React Native vs native development is a critical decision when building a mobile app. Both approaches have their advantages, and the right choice depends on your business goals, budget, timeline, and performance requirements. This guide breaks down the differences, benefits, and ideal use cases to help you make the right decision. What […]
React native Experts

Introduction: React Native continues to evolve to support better performance, improved scalability, and more efficient communication between JavaScript and native platforms. The introduction of the React Native New Architecture represents a major step forward in how mobile applications are built. Migrating to the new architecture helps developers improve app performance, reduce latency, and take advantage […]
React native Experts

Introduction: The demand for diet and nutrition app development is growing fast as healthcare providers, startups, wellness brands, and connected device companies seek smarter digital solutions. Users now expect personalized nutrition plans, progress tracking, wearable syncing, and expert guidance in one easy-to-use app. For businesses, this creates a major opportunity to improve engagement, build recurring […]
React native Experts

Introduction: Every successful app started as a simple idea, but the graveyard of failed startups is filled with products that were built too big, too slow, and without checking to see if there was any real market demand. That’s why partnering with the right MVP app development company can be the most important decision you […]
React native Experts

Introduction: B2B mobile applications are changing how businesses communicate, manage operations, serve customers, and collaborate with partners. From sales teams and distributors to suppliers and enterprise customers, mobile apps can make complex business processes more accessible and efficient. Unlike consumer apps, B2B mobile applications are usually designed around specific business workflows, user roles, permissions, integrations, […]
React native Experts

Introduction: E-commerce customers expect more than a mobile-friendly store. They want a shopping experience that is easy to navigate, fast to use, secure, and convenient from product discovery through checkout. A well-planned mobile ecommerce app can bring browsing, payments, order management, customer accounts, and post-purchase updates into one experience. But building an app is not […]
React native Experts

Introduction: Launching a mobile application from scratch can require significant investment in product planning, design, development, testing, infrastructure, and maintenance. For businesses that need a proven app foundation without building every component from the ground up, white label mobile app development can provide an alternative. A white label mobile app is typically developed from an […]
React native Experts

Introduction: The food delivery industry continues to grow as consumers increasingly prefer ordering meals through mobile applications rather than visiting restaurants or placing orders by phone. Customers now expect fast ordering, real-time delivery tracking, multiple payment options, and seamless user experiences. As a result, restaurants, cloud kitchens, startups, and food delivery businesses are investing heavily […]
React native Experts

Introduction: Online learning has become part of our everyday routines. From learning in virtual classrooms to professionals taking up mobile courses and training employees with digital learning solutions, everyone’s looking for flexible learning options. It’s essential for organizations to provide simple, interactive, and on-the-go mobile learning apps to meet the demand. A well-built eLearning app […]
React native Experts

Introduction: Businesses today must build quality, low-cost mobile apps in shrinking timelines. There are three main models to consider when building mobile apps: in-house builds, outsourcing, and nearshore development. Nearshore development allows businesses to work with software teams located in nearby countries, often within similar time zones and cultural environments. This approach combines many of […]
React native Experts

Introduction: Music streaming app development focuses on creating digital platforms that allow users to stream, discover, download, and share music seamlessly across devices. With the growing demand for on-the-go entertainment, music streaming apps have become one of the most popular mobile applications worldwide. From startups launching niche audio platforms to enterprises building Spotify-like solutions, a […]
React native Experts

Introduction: Entertainment has moved far beyond traditional television, cinema, radio, and physical media. People now discover, watch, listen to, share, and interact with content through mobile applications. From video streaming and music platforms to podcasts, live events, social entertainment, creator platforms, and interactive media, users expect content to be available quickly, easy to discover, personalized, […]
React native Experts

Introduction: The demand for doctor appointment app development is rising rapidly as healthcare organizations modernize patient access and streamline scheduling operations. Patients now expect the convenience of booking appointments, receiving reminders, accessing telehealth visits, and managing healthcare interactions directly from their smartphones. For healthcare businesses, this creates a major opportunity to improve patient satisfaction, reduce […]
React native Experts

Introduction: Users today expect to book rides instantly, track drivers in real time, make secure payments, and manage trips directly from their smartphones. Traditional taxi booking systems and manual dispatch operations are no longer enough to meet modern customer expectations. This shift has made taxi app development one of the fastest-growing sectors in mobile technology. […]
React native Experts

Introduction: hoosing the right fintech app development company is an important decision for businesses planning to launch digital banking platforms, mobile payment solutions, investment applications, digital wallets, or lending products. The development partner you select can influence your application’s security, scalability, user experience, and ability to integrate with financial services. Unlike many standard mobile applications, […]
React native Experts

Introduction: Transportation is becoming increasingly digital. Customers now expect real-time tracking, instant booking, accurate ETAs, cashless payments, and seamless communication directly from their smartphones. Whether it is ride-sharing, fleet management, public transit, logistics, or delivery coordination, mobile technology is transforming how transportation businesses operate. That is why transportation app development has become a major investment […]
React native Experts

Introduction: The home services industry is rapidly moving toward digital convenience. Customers no longer want to spend hours searching for plumbers, electricians, carpenters, painters, or repair professionals through phone directories and local advertisements. Instead, they expect to book trusted service providers instantly through mobile applications. This growing demand has made handyman app development one of […]
React native Experts

Introduction: React Native app development cost is one of the most searched topics for startups, enterprises, and product owners planning cross-platform mobile applications. Businesses want to understand how much it costs, what factors influence pricing, and whether React Native is cost-effective compared to native development. This guide breaks down React Native app development pricing, cost […]
React native Experts

What Is React Native Paper Drawer? React Native Paper Drawer is a Material Design-styled drawer component provided by the react-native-paper library. It is commonly used with React Navigation to build a side navigation menu (sidebar) in React Native apps. It is ideal for: Admin panels Dashboard apps Multi-screen mobile applications Material Design–based UI When to […]
React native Experts

Introduction: Planning a trip usually involves several separate activities: searching for destinations, comparing stays, booking transportation, managing itineraries, checking maps, and keeping track of reservations. A well-designed travel mobile app can bring many of these tasks together and make the travel experience more convenient before, during, and after a trip. For travel businesses, however, building […]
React native Experts

Introduction: Healthcare is becoming more accessible, convenient, and technology-driven than ever before. Patients today expect to order medicines online, upload prescriptions digitally, track deliveries in real time, and receive healthcare products directly at their doorstep. As consumer expectations continue evolving, pharmacies and healthcare providers are increasingly investing in medicine delivery applications to improve service quality […]
React native Experts

Introduction: The way customers discover restaurants, view menus, place orders, make reservations, and interact with food businesses has increasingly moved to mobile devices. A well-designed restaurant mobile app can bring these experiences together in one convenient platform while also helping restaurants manage orders, customers, payments, promotions, and loyalty programs. Restaurant mobile app development is not […]
React native Experts

Introduction: Building a mobile app today often means reaching users on both iOS and Android. For many businesses, developing separate applications for each platform can increase costs, extend timelines, and create ongoing maintenance challenges. This is where React Native for Mobile App Development has become a popular choice. Developed by Meta, React Native allows businesses […]
React native Experts

Introduction: Consumer shopping habits have changed dramatically over the last few years. Today’s customers expect groceries to be delivered directly to their homes with just a few taps on a smartphone. Convenience, speed, and real-time accessibility have become major factors influencing purchasing decisions. As a result, grocery delivery applications have become an essential digital solution […]
React native Experts

Introduction: Ordering food has become a digital experience that involves much more than selecting a meal and clicking “order.” Customers expect to discover restaurants quickly, customize meals, choose a payment method, receive accurate order updates, and track deliveries without having to call the restaurant. Behind that simple customer experience is a much more complex system […]
React native Experts

Introduction: In todays modern digital economy, enterprises are no longer relying on one-size-fits-all software. They’re investing in custom app development to create solutions that align with their exact business workflows, security policies, and scalability needs. Enterprise software solutions play a central role in enabling organizations to design, deploy, and maintain powerful applications that drive efficiency, […]
React native Experts

Introduction: In 2026, React Native remains the top choice for building fast, scalable, and cost-effective mobile apps for both iOS and Android. Businesses are increasingly hiring React Native app development companies that offer deep technical expertise, flexible engagement models, and full-cycle development from product design to post-launch support. Here’s a curated list of the best […]
React native Experts

Introduction: The financial industry is undergoing a massive transformation driven by fintech innovation. From mobile payments to AI-based investing, fintech app development empowers businesses to deliver smarter, faster, and safer digital financial services. What Is Fintech App Development? Fintech app development is the process of designing and building digital platforms that allow users to perform […]
React native Experts

Introduction: Social media is now a core part of the daily life of millions of users in today’s digital world. Whether people are sharing stories or solving problems with friends, the average person turns to some form of social media for just over an hour each day. If you are an enterprise or a new […]
React native Experts

Introduction: Finding the right Android app developer is about much more than finding someone who can write Android code. A successful application needs thoughtful UI/UX, reliable architecture, secure APIs, device compatibility, performance optimization, testing, and ongoing maintenance. Whether you are launching a startup MVP, building a customer-facing application, developing an enterprise platform, or modernizing an […]
React native Experts

Introduction: Building a mobile app is rarely just a matter of writing code. We need product strategy, UI/UX design, mobile development, backend engineering, testing, security, deployment, and ongoing maintenance. For many businesses, hiring an entire in-house team for all these responsibilities is not practical. That is where outsourcing mobile app development can make sense. When […]
React native Experts

Introduction App development is evolving faster than ever. From startups to enterprises, everyone is looking for frameworks that make mobile and web apps faster, more secure, and more scalable. Choosing the right programming framework can save you time, cut costs, and deliver a smoother user experience. In this artcle, we’ll explore the top 10 programming […]
React native Experts

Introduction In today’s fast-paced world, convenience and luxury go hand in hand. Whether it’s business executives, travelers, or VIP clients, people now prefer comfortable rides with professional chauffeurs instead of regular taxis. This growing demand has made chauffeur app development a popular choice for businesses that want to deliver high-end, tech-driven travel experiences. If you’re […]
React native Experts

Introduction Startups are about creating, speed and scaling big. Yet, developing a great mobile app is all about the right talent, some serious experience and the correct creation strategy. Choosing the best app developers for startups can make the difference between an app that finds its market and one that doesn’t. So, Whether you’re launching new product or service, […]
React native Experts

Introduction: People are increasingly comfortable handling everyday services through their phones, and healthcare is no different. Instead of waiting on hold or travelling to a clinic for every consultation, patients can use an on-demand doctor app to find a suitable healthcare professional, book an appointment, attend a virtual consultation, and manage follow-up information from one […]
React native Experts

Introduction: The way people consume content has completely changed. Users no longer want to depend on traditional television schedules or desktop-only media platforms. Today, people expect instant access to movies, live events, educational content, gaming streams, podcasts, and entertainment directly from their mobile devices. This shift has made video streaming app development one of the […]
React native Experts

Introduction: When building modern mobile apps with React Native, user-friendly input components play a huge role in creating smooth experiences. One common requirement is allowing users to select multiple items from a list, often grouped into categories. That’s where React Native Sectioned Multi Select comes in. This popular open-source package simplifies the process of building […]
React native Experts

Introduction E-learning is an important part of both education and professional development in today’s fast-paced digital world. Apps on mobile are changing the way people learn, from schools to business training programs. It’s important to understand e-learning mobile app development and work with the right e-learning app development company if you want to make a […]
React native Experts

Introduction Businesses today need employees, customers, partners, and field teams to access information and complete tasks from anywhere. Enterprise mobile applications can bring these workflows onto mobile devices while connecting users with the business systems they already rely on. But enterprise mobile app development is very different from building a simple consumer app. Enterprise applications […]
React native Experts

Introduction Real estate businesses are increasingly using mobile applications to help buyers discover properties, connect with agents, schedule visits, and manage transactions. But a successful real estate app is more than a property listing platform. Modern applications need accurate property data, location services, advanced search, secure communication, notifications, media-rich listings, and reliable backend systems. In […]
React native Experts

Introduction In today’s digital-first world, people are more in tune now than ever with taking care of their physical, mental and emotional health. From fitness monitoring and meditation exercises to food planning and tension control, the wellness app is widely accepted as a daily fixture. For businesses, startups and healthcare providers, wellness app development is […]
React native Experts

Introduction Healthcare is one of the fastest-growing industries when it comes to adopting digital solutions. Patients expect faster access to doctors, medical reports, and healthcare services, while hospitals and clinics look for ways to streamline operations and improve efficiency. This has made healthcare mobile app development services an essential part of modern medical practices. Whether […]
React native Experts

Introduction Launching a startup is exciting, but turning an idea into a successful mobile app can feel overwhelming. From validating the concept to designing, developing, and launching, app development for startups requires careful planning and the right technical expertise. In today’s digital world, startups that leverage mobile technology gain a significant edge. Whether it’s a […]
React native Experts

Introduction In the last 10 years, the travel and tourism industry has changed a lot. Smartphones are becoming such a big part of everyday life that tourists use mobile apps to book flights, find hotels, explore new places, and even keep track of their vacation plans. This change has opened up a huge chance for […]
React native Experts

Introduction When developing mobile apps, a smooth navigation experience is one of the most important factors that keep users engaged. In React Native, one of the most commonly used UI elements for navigation is the AppBar (sometimes called a header or toolbar). The React Native AppBar plays a vital role in making apps look professional, […]
React native Experts

Introduction The way people buy groceries has changed. Customers no longer want to visit multiple stores, wait in long checkout lines, or spend time searching for products manually. They expect groceries to be available through a fast and simple mobile experience. That is why grocery mobile app development has become a major focus for supermarkets, […]
React native Experts

Introduction Sports fans today do not just watch games. They want to be part of the action. From checking live scores to joining fantasy leagues and streaming matches on their phones, fans are more connected than ever. This makes sports apps essential for teams, leagues, and businesses that want to grow their audience and revenue. […]
React native Experts

Introduction In today’s marketplace, mobile apps have become a necessity for companies of all sizes right from those in startups to larger multinational corporations. But developing a high-quality application that works seamlessly on both iOS and Android isn’t cheap or fast if you’re only using internal resources. This is where React Native development outsourcing plays […]
React native Experts

Introduction The logistics industry has changed dramatically over the past decade. Customers expect real-time shipment updates, businesses want complete visibility into their supply chains, and logistics companies are under constant pressure to deliver faster while controlling operational costs. Meeting these expectations isn’t easy when operations rely on spreadsheets, phone calls, or disconnected software systems. That’s […]
React native Experts

Introduction Building a mobile app no longer requires businesses to hire and manage a large in-house development team. With offshore React Native app development, companies can work with experienced developers from another country to build, launch, and maintain iOS and Android applications while keeping development flexible. React Native is a popular choice for businesses that […]
React native Experts

Introduction A successful mobile application is rarely built by one person. Behind a reliable app is usually a mobile app development team with different specialists responsible for product planning, UI/UX design, development, testing, deployment, security, and ongoing maintenance. The size and structure of that team depend on the application. A simple MVP may need only […]
React native Experts

Introduction The fitness app market has never been more competitive. Every month, hundreds of new workout apps, nutrition platforms, wellness trackers, and personal training solutions appear on the App Store and Google Play. Yet only a small percentage manage to build an active user base that sticks around for months rather than uninstalling the app […]
React native Experts

Introduction Software as a Service has changed how businesses buy and use software. Instead of installing a program once and paying for a permanent license, customers can access a SaaS product online and pay through a subscription or usage-based model. That sounds simple from the outside. Behind the scenes, however, a SaaS product needs to […]
React native Experts

Introduction If you’re planning to build a cross-platform mobile app, you’ve probably come across two popular names: Ionic and React Native. Both let you create apps for iOS and Android using a single codebase, but they work in different ways and serve different needs. In this article, we’ll break down the key differences between Ionic […]
React native Experts

Is Material UI helpful for building React Native apps as fast as possible? Absolutely. With Material UI for React Native, powered by React Native Paper, developers can access pre-designed components that follow Google’s Material Design system. This allows for faster development and elegant interfaces — without having to reinvent the wheel. At React Native Experts, […]
React native Experts

Introduction Turning your product idea into a reality is best done with a strategy, and MVP (Minimum Viable Product) development allows businesses to test their idea with early adopters and validate their concept. Also, it reduces risk – all without committing to over-budgeting a large-scale development project. In order to achieve this, a well-equipped framework […]
React native Experts

Introduction Choosing the right hybrid app development company can help businesses launch mobile applications across iOS and Android without maintaining two completely separate development projects. However, the right solution depends on your app’s features, performance requirements, budget, and long-term growth plans. At React Native Experts, we help businesses evaluate cross-platform mobile development approaches and build […]
React native Experts

Introduction In the world of React Native development, choosing the right state management solution plays a crucial role in creating smooth, high-performance applications. While Redux has long been the go-to library for many developers, its complexity and boilerplate have driven developers to search for simpler alternatives. This is where Zustand steps in—a minimalistic yet powerful […]
React native Experts

Introduction Events in the modern world are more than just an occasion to celebrate something; they bring people together and require meticulous planning, constant interaction, and management in the digital world. Every type of event, be it a concert, seminar, wedding, or a corporate meeting, has a mobile solution that can significantly improve the success […]
React native Experts

Introduction Hiring the right mobile app developer can have a major impact on your application’s quality, development timeline, scalability, and long-term maintenance. A developer may have strong programming skills, but that does not necessarily mean they are the right fit for your specific product. The best hiring process starts by defining your requirements, choosing the […]
React native Experts

Introduction In today’s mobile-first world, a seamless and intuitive navigation experience is not just a feature—it’s a user expectation. Whether it’s a social app, a wellness tracker, or an eCommerce platform, users want quick, familiar access to key sections of your app. The React Native bottom navigation bar provides exactly that—speed, clarity, and control, packaged […]
React native Experts

Introduction In today’s mobile-centric world, where mobile devices are so important, making a mobile app is becoming more and more important, if not necessary. No matter if you’re a new business or an old one, the first step is usually to search Google for “mobile app development company near me.” I get where you’re coming […]
React native Experts

Introduction The way people manage insurance is changing. Customers no longer want to depend entirely on phone calls, paperwork, or branch visits to check a policy or submit a claim. They expect to access insurance services from their phones, just like they manage banking, shopping, and other everyday activities. This is where insurance app development […]
React native Experts

Introduction In today’s fast-paced digital economy, businesses in eCommerce, food delivery, and parcel logistics can no longer afford to operate without a robust and scalable delivery application. Such apps streamline order placement, enable real-time tracking, and deliver instant notifications—improving both customer experience and operational efficiency. As cross-platform functionality becomes a necessity, React Native stands out […]
React native Experts

Introduction It’s hard to launch a mobile app these days because developers have to deal with many platforms. Companies can’t afford to make separate apps for Android and iOS anymore, not when time, money, and growth are on the line. This is where cross-platform development comes in handy: you can build once and deploy everywhere […]
React native Experts

Introduction Writing code is only one part of building a successful mobile application. A React Native project can have clean architecture, a modern interface, and experienced developers, yet still fail to create meaningful business results if the product strategy is unclear. Successful React Native development starts by connecting technology decisions with business goals, user needs, […]
React native Experts
Introduction Mobile apps are the backbone of business as enterprises become digitized, which benefits business growth. From internal productivity tools to frontend customer-facing apps, mobile is powering efficiency, engagement, and competitive advantage. Enterprise mobile app development is all about creating powerful, secure, and scalable mobile applications designed for complex organization requirements. Enterprise mobile apps are fundamentally different […]
React native Experts
Introduction Today, the digital world moves fast, and a generic app won’t do the job anymore. Whether you are a fresh startup, a growing small-to-medium enterprise (SME), or a major firm trying to polish efficiency, your software has to match your unique rules, customer habits, and brand voice. That is precisely why bespoke app development […]
React native Experts
Why Login Matters in Modern Mobile Apps In today’s world, where mobile devices are so important, user login isn’t just a feature; it’s the key to safe, personalized experiences. It’s important to have secure and reliable authentication in place whether you’re making a social app, an e-commerce site, or a fitness tracker. The Parse SDK […]
React native Experts

Introduction Have you ever used an app on your phone and then opened it on your laptop or tablet without any problems? If so, you were probably using a cross-platform apps. These are apps designed to work on different devices like Android phones, iPhones, Windows computers, and even web browsers. In this article, you will […]
React native Experts

Introduction In today’s digital world, customers expect fast, easy and personalized shopping experiences. Whether you own a small shop or a large retail chain, having a mobile app can help your business grow. Retail app development is changing how businesses sell their products and connect with customers. A mobile app makes it easier for customers […]
React native Experts
Introduction Building a mobile app involves much more than writing code. Businesses need to validate an idea, understand user requirements, select the right technology, plan the architecture, estimate development costs, and prepare the application for long-term growth. Making the wrong technical decision early can lead to higher development costs, performance problems, and difficult maintenance later. […]
React native Experts

What is React Native Expo? React Native Expo is a framework and platform within the React Native ecosystem that facilitates easier development, building, and deployment of cross-platform mobile applications. For both developers and businesses, React Native Expo offers a set of tools and services that, in contrast to other platforms, do not require complicated custom […]
React native Experts

Introduction: The cost to develop a fantasy sports app in 2026 can vary significantly depending on the sports covered, number of platforms, real-time features, payment systems, third-party integrations, and overall application complexity. A basic fantasy sports app may require only essential contest and team-management features, while a large-scale platform can involve real-time scores, live leaderboards, […]
React native Experts

Introduction: In today’s digital world, video calling is an essential feature for many mobile apps. Whether doctors consult patients online, teachers hold virtual classes, or support teams help customers, real-time communication is key. If you’re planning to build a video-enabled mobile app, consider using React Native development services to ensure a fast and reliable experience. […]
React native Experts
Introduction: Are you looking to build a mobile app that works on both Android and iOS without breaking the bank? An offshore cross-platform app making service is the perfect solution. It helps businesses like yours develop high-quality mobile apps quickly, efficiently, and affordably, all with just one codebase. In this guide, we’ll explain what offshore […]
React native Experts

Introduction: Today, mobile apps play a huge role in helping businesses grow. From small startups to big companies, almost everyone wants a mobile app. But building an app can be costly and time-consuming, especially when hiring developers locally. This is where offshore mobile app development comes in. It helps businesses get quality apps at lower […]
React native Experts
Introduction: We are currently experiencing a world dominated by mobile applications. From ordering food and hailing a cab to managing finances and keeping track of health, everything is just a tap away. Meeting the demand and expectations of users has become easy. However, along with providing the satisfaction, technology also pushes the boundary and raises […]
React native Experts
Introduction: The world of mobile app development is advancing quickly, and the phrases Firebase vs React Native should not be new to you. They sound alike at first, but in reality, they have complex distinctions that serve different functions. In this article, we will explore the core functions of each tool, their usages in the […]
React native Experts
Introduction: In today’s mobile app landscape, real-time navigation, detailed mapping, and location intelligence are more than just features—they are core to user experience in apps like ride-hailing, logistics, food delivery, and travel. While Google Maps is a popular choice, HERE Technologies offers a powerful and flexible SDK that gives developers advanced control over maps, routing, […]
React native Experts
Introduction: In today’s mobile app landscape, real-time navigation, detailed mapping, and location intelligence are more than just features—they are core to user experience in apps like ride-hailing, logistics, food delivery, and travel. While Google Maps is a popular choice, HERE Technologies offers a powerful and flexible SDK that gives developers advanced control over maps, routing, […]
React native Experts
Introduction: In-app navigation has evolved from simple direction lines on maps to full-fledged systems with voice-guided turn-by-turn navigation, real-time traffic awareness, offline capabilities, and custom UI controls. For React Native developers, Mapbox emerges as a robust and highly customizable alternative to Google Maps, especially for applications that need more design freedom or offline functionality. In […]
React native Experts
Introduction Fantasy sports have transformed from being an online game into a full-fledged platform with advanced features that attract thousands of players around the world. Today’s platforms are real-time engagement engines, part strategy game, part social network, part live sports companion, and the apps that win are the ones that keep pace with what users […]
React native Experts
Introduction: React Native is one of the most popular frameworks for building mobile apps using a single codebase. With each new release, it gets more stable, powerful, and performance-oriented. React Native 0.75 is no different—it brings meaningful updates aimed at improving developer experience, performance, and compatibility with the latest mobile platforms. In this article, we’ll […]
React native Experts
Introduction: React Native has been a game-changer for cross-platform mobile development, enabling developers to build apps for iOS and Android with a single codebase using JavaScript and React. Over the years, React Native has continuously evolved to improve performance, scalability, and developer experience. Two major improvements that promise to significantly enhance performance and offer better […]
React native Experts
Introduction: One of the biggest challenges in mobile app development is keeping the app size minimal while maintaining performance and functionality. A large app size can lead to higher download times, increased storage usage, and poor user experience—ultimately affecting retention rates. React Native apps, by default, include various dependencies, assets, and libraries that can bloat […]
React native Experts
Introduction: Performance and UI consistency are crucial in mobile app development. A well-optimized UI can significantly impact user engagement, retention, and overall app success. When building React Native applications, achieving both high performance and a beautiful UI can be challenging due to unnecessary re-renders, inefficient style processing, and layout shifts. This is where Gluestack UI […]
React native Experts
Introduction: Testing is an essential part of mobile app development, ensuring that applications are stable, reliable, and function as expected. In the React Native ecosystem, there are numerous testing tools available for various sorts of testing, including unit testing, integration testing, and end-to-end testing. Jest is the greatest of these tools since it is quick, […]
React native Experts
Introduction: Storybook is a powerful tool that enables developers to build UI components in isolation, making UI development, testing, and documentation much easier. In React Native, Storybook helps visualize different states of a component without running the entire app. This blog provides a complete guide on setting up and using Storybook with React Native. This […]
React native Experts
Introduction: Developing a successful mobile application is more than writing code; it’s also focusing on values such as user experience. That is where Pendo and React Native contribute. While Pendo enables user behavioral analytics, feedback collection, and in-app support documentation without the need for additional coding, React Native allows developers to create applications that function […]
React native Experts
Introduction: In today’s fast-paced digital world, building scalable, feature-rich mobile applications is no longer a luxury—it’s a necessity. However, developing such apps can be challenging, especially when it comes to managing backend infrastructure, authentication, and real-time data synchronization. Enter React Native and AWS Amplify, two powerful tools that, when combined, can help you build robust, […]
React native Experts
Introduction Mobile apps need to launch quickly and work across iOS and Android devices with low long-term costs. There’s becoming more demand for such mobile apps and user expectations are climbing too. People expect: Fast app performance Seamless user experiences Frequent updates Real-time functionality Consistent design across devices This is one of the biggest reasons […]
React native Experts
Introduction Building a mobile app is no longer just about putting a business on the App Store or Google Play. For most companies, the app becomes an important part of how customers discover products, book services, communicate with a business, make payments, or manage their daily activities. The challenge is building an application that works […]
React native Experts
Introduction Building an app for both iOS and Android does not always mean maintaining two completely separate development projects. Cross platform app development allows businesses to share application code, business logic, components, and development resources across platforms while still supporting platform-specific functionality when the product needs it. This approach can be especially useful for startups […]
React native Experts
What is Background Geolocation? Background geolocation is a function within a mobile application that enables tracking of the users’ location when an app runs in the background. It is pertinent to applications such as delivery service systems, fitness trackers, transportation and logistics management systems. For example, background geolocation integration with React Native is seamless with […]
React native Experts
Introduction If you are looking to develop interactive mobile apps, React Native is the best solution. Not only can developers create high-quality touch-based UIs, but they are also able to enhance the usability of the app’s interactivity features. It also consists of a very useful library called ‘React Native Gesture Handler’ that allows the creation […]
React native Experts
Introduction Cross-platform app development has evolved from a cost-saving alternative into a strategic business decision. In 2026, organizations are no longer asking whether cross-platform frameworks can deliver high-quality mobile experiences. Instead, they are evaluating which framework provides the best balance of performance, scalability, development speed, and long-term maintainability. As mobile applications become increasingly central to […]
React native Experts
Introduction React Native is a powerful framework that allows developers to build mobile apps for iOS and Android using a single codebase. Its growing popularity is supported by a vibrant community and numerous libraries that make app development faster, easier, and more efficient. If you’re looking to create a high-performing mobile app, leveraging the right […]
React native Experts
Introduction When building a React Native app that requires users to access photos or videos from their device’s gallery, integrating the @react-native-camera-roll/camera-roll library is a great solution. This library provides an easy way to access and manage the media on the user’s device. In this article, we’ll walk through the steps to implement photo and […]
React native Experts
Introduction to Implement OTP Verification in React Native Apps In today’s digital world, security is essential, and OTP (One-Time Password) verification is a highly effective way to protect users’ accounts in mobile apps. It ensures that only authorized users can access their accounts by sending a unique code to their devices. In this article, we’ll […]
React native Experts

Introduction to React Native React Native is a powerful open-source framework that developers use to build mobile apps for iOS and Android using JavaScript and a single codebase. Building a React Native app with video playback is common for eLearning platforms, OTT apps, fitness solutions, social media products, and internal training tools. The most widely […]
React native Experts
Unlock the power of Google Play Console to manage apps, analyze performance, and reach a global audience with powerful insights and tools.
React native Experts
Introduction: In today’s mobile-first world, where smartphone applications are an integral part of our daily lives, ensuring that your app delivers an intuitive and powerful camera experience is paramount. Imagine this scenario: a user downloads your app, eager to capture a moment, but is met with a clunky camera interface or, worse, poor image quality. […]
React native Experts
Introduction: In the fast-paced world of mobile app development, real-time communication is essential. One of the most effective ways to achieve this is by integrating MQTT (Message Queuing Telemetry Transport) with React Native. MQTT is a lightweight messaging protocol designed for real-time communication, particularly in environments with limited bandwidth or high latency. This blog will […]
React native Experts
Introduction: In today’s digital age, users expect real-time updates, instant notifications, and seamless communication across devices. Whether it’s chatting with friends, collaborating on documents, or following stock market trends, the need for instantaneous data exchange has become crucial. Traditional HTTP-based systems often struggle to meet these real-time expectations due to inherent limitations in how they […]
React native Experts
Introduction: Unity is a powerful game engine widely used to create immersive 2D and 3D experiences, while React Native is a popular framework for building cross-platform mobile applications using JavaScript. Integrating Unity with React Native allows developers to enhance mobile apps with advanced 3D graphics, augmented reality (AR), and virtual reality (VR) capabilities while maintaining […]
React native Experts
Introduction: Shopify Mobile App with React Native is a powerful solution as mobile commerce continues to rise. Businesses must cater to their customers’ preferences for seamless, user-friendly shopping experiences. Shopify, a leading e-commerce platform, empowers businesses to set up online stores effortlessly. However, the user experience can be elevated further through a mobile app. With […]
React native Experts
Introduction: React Native Paper is a popular UI framework that makes it simple for developers to design user interfaces that are highly dynamic, visually beautiful, and consistent. It provides an extensive collection of pre-designed elements, such as buttons, cards, dialogs, and more, and is based on Google’s Material Design principles. This enables developers to concentrate […]
React native Experts
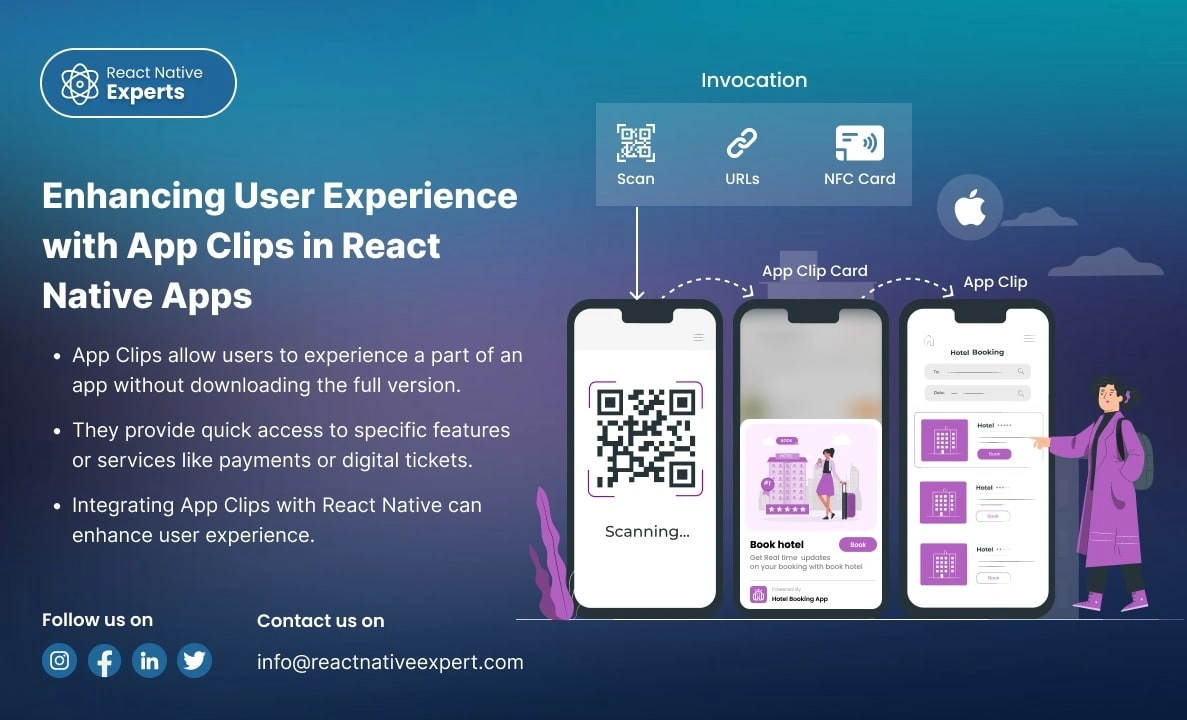
Introduction: App Clips provides a revolutionary way for users to experience a small part of your app without downloading the full version. Apple’s App Clips, introduced in iOS 14, are designed to offer users a streamlined way to interact with an app without requiring them to install it fully. With App Clips, you can offer […]
React native Experts
Introduction: In an era where real-time communication is crucial for the success of many applications, WebRTC (Web Real-Time Communication) emerges as a powerful tool that enables peer-to-peer audio, video, and data sharing within browsers and mobile applications. This blog will dive deep into how you can leverage WebRTC in React Native to build feature-rich communication […]
React native Experts
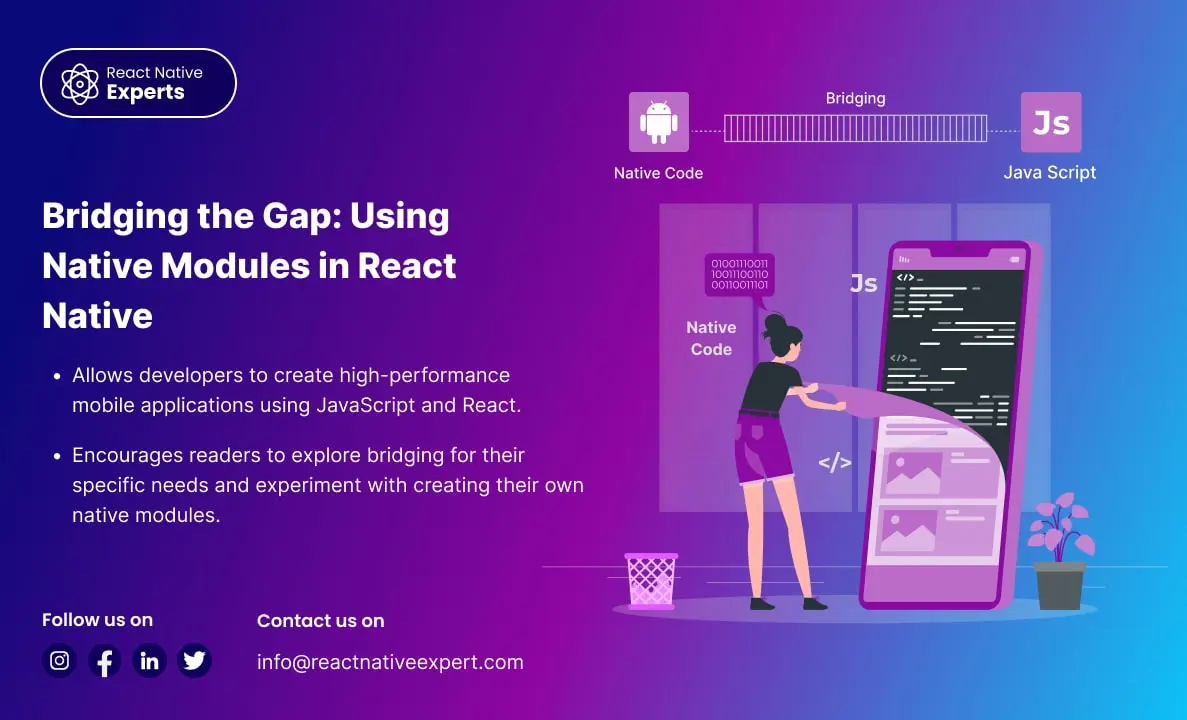
Introduction: React Native has transformed mobile app development by enabling developers to build cross-platform applications using a single JavaScript codebase. While it covers most common use cases out of the box, some advanced device capabilities and performance-intensive features still require direct access to native APIs. This is where native modules in React Native play a […]
React native Experts
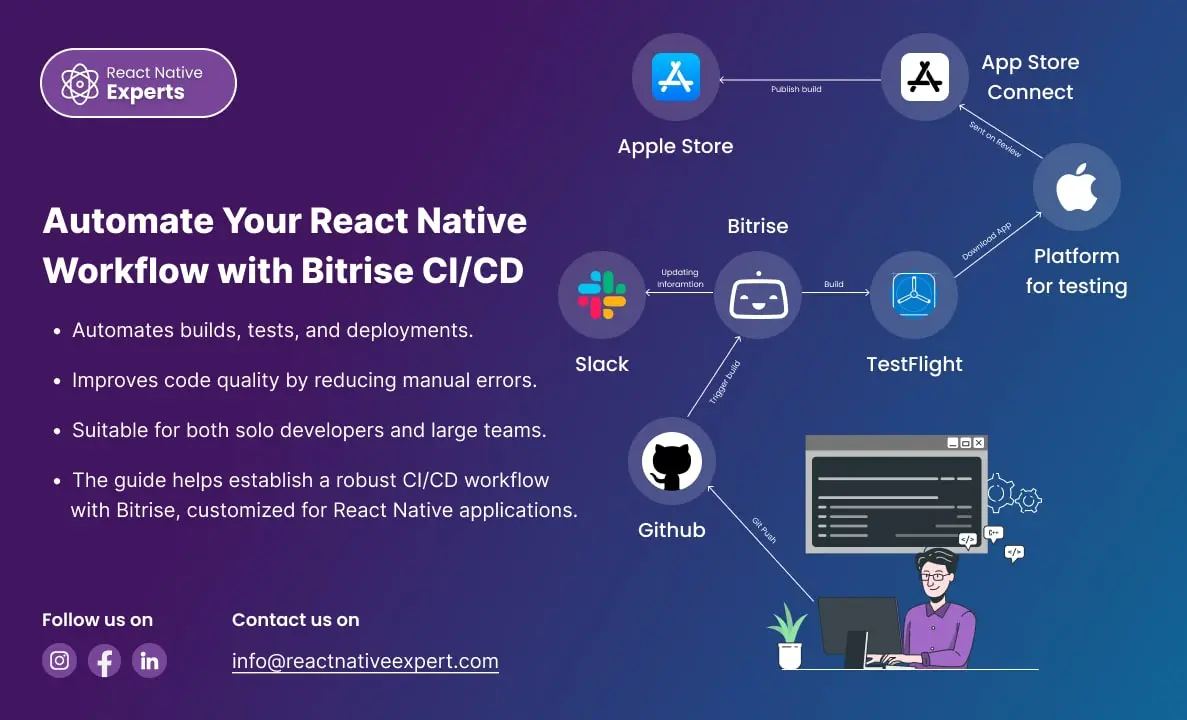
Introduction: In today’s fast-paced development environment, Continuous Integration (CI) and Continuous Deployment (CD) are essential for delivering high-quality software quickly. Bitrise is a leading CI/CD platform tailored for mobile apps, offering seamless integration with React Native. This blog will walk you through the process of setting up Bitrise for a React Native project, including code […]
React native Experts
https://reactnativeexpert.com/wp-content/uploads/2024/07/Codepush.mp4#t=1 Introduction: CodePush is a cloud service from Microsoft that enables React Native developers to deploy mobile app updates directly to their users’ devices. This bypasses the traditional app store update process, providing a seamless way to fix bugs, add features, and make other changes without the need for users to download a new version […]
React native Experts
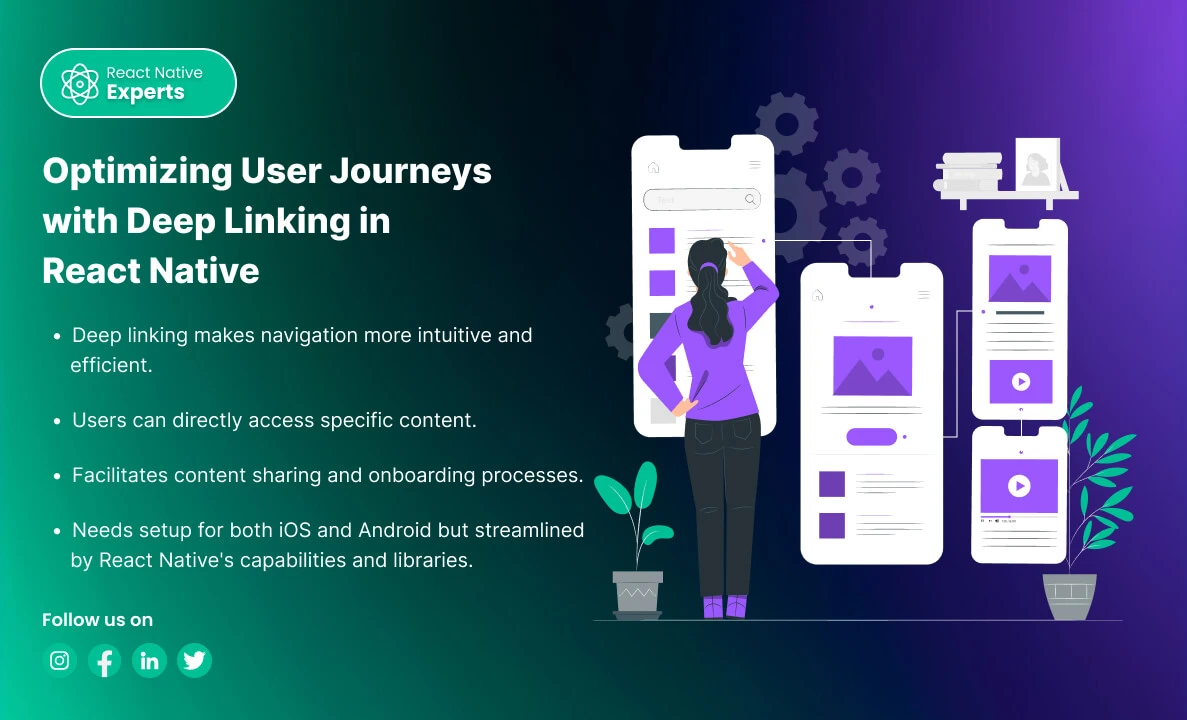
Introduction: A mobile app can have hundreds of screens, but users rarely want to start from the home screen and navigate through several menus just to reach the information they need. Imagine a customer receives a link to a product in an email. Instead of opening the app and searching for that product manually, the […]
React native Experts
Introduction: White-labeling is a process where a product or service produced by one company is rebranded by another company to make it appear as its own. In the context of mobile applications, white labeling allows businesses to customize an app’s appearance and functionality to match their brand without developing an app from scratch. React Native, […]
React native Experts
Introduction: In the dynamic landscape of mobile development, efficient data handling is paramount for creating high-performance applications. Realm Database stands out as a powerful solution for React Native developers, offering a blend of speed, simplicity, and offline capabilities. In this blog, we’ll explore why Realm is a top choice, how to manage offline data in […]
React native Experts
Introduction: When building mobile applications, managing data efficiently and ensuring offline capabilities are critical to delivering a smooth user experience. SQLite Database is a reliable and powerful choice for React Native developers. This blog will cover why SQLite is a top choice, how it facilitates offline data management, setup instructions (with description and query examples), […]
React native Experts
Introduction: In the realm of modern mobile applications, Bluetooth Low Energy (BLE) stands out as a crucial technology for enabling efficient, wireless communication between devices. Whether you’re developing health monitors, smart home gadgets, or industrial IoT solutions, understanding how to integrate BLE with React Native can significantly enhance your app’s capabilities. This professional blog explores […]
React native Experts
Introduction: GraphQL has emerged as a powerful tool for querying APIs, providing an efficient and flexible alternative to REST. When combined with React Native, it can significantly enhance mobile app development. In this blog, we’ll explore what GraphQL is, why it’s beneficial for React Native, how to connect it with a React Native app, and […]
React native Experts
Introduction: As mobile commerce continues to grow, integrating secure and efficient payment methods into your app becomes crucial. Apple Pay and Google Pay are two leading digital wallets that offer users a seamless payment experience. This guide explores why you should integrate these payment options into your React Native app, how to do it, and […]
React native Experts
Introduction: In today’s digital era, seamless Payment Solutions and secure payment processing are essential for the success of any mobile application that involves financial transactions. Integrating a payment gateway into your React Native app can greatly enhance user experience, security, and trust. This blog will explore why you should use a payment gateway and when […]
React native Experts
Introduction: In today’s fast-paced digital landscape, businesses need to quickly develop and deploy applications to stay ahead of the competition. Combining the low-code development capabilities of Mendix with the powerful mobile framework React Native can significantly accelerate the development process. This blog will explore what Mendix is, how to work with it, how to connect […]
React native Experts
Introduction: React Native has become a go-to framework for building sleek and responsive mobile apps. But what if you want to add that extra layer of interactivity—real-time updates, live data feeds, or instant messaging? That’s where Socket.IO comes in, and React Native experts can leverage its power to create truly engaging user experiences. What is […]
React native Experts
Introduction: Building mobile apps, especially with React Native, is fantastic! You can create beautiful, native-feeling apps for both Android and iOS with a single codebase. But even the most talented React Native developers know that debugging these apps can be a real challenge. Imagine a user happily browsing your app when suddenly it crashes. Frustrated, […]
React native Experts
Introduction: React Native has changed significantly over the last few years. What started as a way to share mobile application development across iOS and Android has evolved into a more modern framework with a new architecture, improved tooling, stronger native integration, and a more mature development ecosystem. In 2026, following React Native trends is not […]
React native Experts
Introduction: React Native continues to evolve rapidly, empowering React Native experts to build even more performant and efficient mobile apps. Keeping up with the latest releases is crucial for staying ahead of the curve. ‘React Native 0.72 vs 0.73 vs 0.74’, In this blog post dive into the key differences between React Native Versions 0.72, […]
React native Experts
Introduction: React Native developers often face the dilemma of choosing the right storage solution for their applications. Two popular options for storing data are MMKV and AsyncStorage. In this article, ‘MMKV vs AsyncStorage in react native’, we’ll conduct a comparative analysis of these two libraries to help you make an informed decision based on your project […]
React native Experts
Introduction: Mobile users expect apps to work instantly. They do not want slow loading screens, confusing navigation, laggy performance, or apps that drain battery life. Whether it is ecommerce, healthcare, SaaS, logistics, or social platforms, mobile experience now directly affects user retention and business growth. That is why mastering mobile optimization has become one of […]
React native Experts
React Native’s Evolution: From 2015 to 2026 When React Native was introduced in 2015, its main attraction was simple: developers could use React to build mobile applications for iOS and Android without maintaining two completely separate codebases. More than a decade later, React Native has changed considerably. It has moved from its original architecture to […]
React native Experts
Introduction: E-commerce is no longer limited to desktop websites. Consumers increasingly expect fast, convenient, personalized shopping experiences that work seamlessly across mobile devices. For businesses, this means a mobile app is becoming an important part of the overall e-commerce strategy. React Native is playing an important role in this shift by allowing businesses to develop […]
React native Experts
Introduction: Devin AI vs. React Native Experts, Let’s delve into the intriguing comparison between React Native experts and Devin AI, the world’s first fully autonomous AI software engineer. As a React Native developer, you’re likely curious about the capabilities of Devin and how it stacks up against human expertise. Buckle up as we explore this fascinating topic! […]
React native Experts
Introduction: For startups, speed and smart spending can decide survival. Building separate apps for iOS and Android often drains time, money, and team energy before product-market fit is even clear. That’s where React Native becomes powerful. With a single codebase, startups can launch on multiple platforms, validate ideas with real users, and iterate fast without […]
React native Experts

Introduction: Mobile app development has changed a lot in the last few years. What used to be a straightforward decision between building separately for iOS and Android has become a much broader conversation. Businesses now expect their apps to be fast, scalable, secure, accessible, and ready to connect with everything from AI services to wearable […]
React native Experts
Introduction: Business growth with React Native is becoming a strategic advantage for startups and enterprises aiming to launch mobile applications quickly, reduce costs, and reach wider audiences. By enabling cross-platform development with a single codebase, React Native helps businesses accelerate digital transformation and improve time-to-market. In the current competitive environment, companies that adopt effective mobile […]
React native Experts
Introduction: Building a mobile app that is fast, scalable, and cost-effective requires the right technology and the right team. This is why many businesses choose to hire React Native experts for their mobile app development needs. With React Native, companies can build apps for both Android and iOS using a single codebase, reducing development time […]
React native Experts

Introduction: React Native Apps have transformed the mobile development market by allowing developers to construct high-quality, cross-platform applications with unprecedented efficiency. As we progress through 2026, React Native’s influence grows across a wide spectrum of applications that are transforming the digital world. From social media behemoths like Instagram and Facebook, which continue to set new […]
React native Experts
Introduction: Every successful mobile app starts with an idea. It could be a solution to an everyday problem, a new way to connect people, or a business concept that has the potential to transform an industry. But turning that idea into a polished mobile application requires the right strategy, technology, and development partner. Today, businesses […]
React native Experts
Introduction: Choosing the right mobile development partner can be one of the most important decisions when turning an app idea into a real product. The right team does more than write code. It should understand your business objectives, target users, technical requirements, budget, timeline, and long-term product goals. With so many mobile development companies and […]
React native Experts
Introduction: In the dynamic world of mobile app development, React Native stands as a beacon of innovation and efficiency, weaving seamless experiences that not only captivate users but also drive sales and income. At React Native Experts, our React Native development prowess takes your unique ideas and transforms them into digital masterpieces. Let’s embark on […]
React native Experts
Introduction: Whenever we push our code in Git, we have to check code syntax issues or code styling. But we often forget these things, so how can we overcome this? The solution is to use an automated tool whenever we push our code changes in Git, it will automatically check syntax or styling issues. For […]
React native Experts
Introduction: In today’s fast-paced world of mobile development, React Native has emerged as a game-changer. This cross-platform framework enables developers to create mobile apps for both iOS and Android with a single codebase. However, like any technology, React Native apps can benefit from optimization to ensure top-notch performance. In this blog post, we’ll explore the […]
React native Experts
Introduction: In today’s fast-paced digital world, creating a seamless and captivating user experience is crucial for the success of any mobile application. React Native, a powerful framework for cross-platform mobile development, has become the go-to choice for businesses and developers looking to create high-quality apps efficiently. In this blog, we’ll delve into the world of […]
React native Experts
Introduction: Cross-platform app development continues growing rapidly in 2026. Businesses want faster launches, lower development costs, and mobile apps that work smoothly on both Android and iOS without maintaining two separate codebases. That is why frameworks like React Native and Flutter remain two of the most discussed technologies in mobile app development. But choosing between […]
React native Experts
Introduction: Fastlane stands out as a pivotal tool in the arsenal of mobile developers, providing a streamlined path for automating the build, test, and deployment processes of mobile applications. For React Native developers, incorporating Fastlane into the workflow is a game changer. It not only enhances efficiency but also ensures consistency across builds, ultimately leading […]
React native Experts
Introduction: In today’s app-driven ecosystem, monetization is a critical element for developers, and in-app purchases stand at the forefront of this drive. However, managing these purchases can be a complex endeavor. This is where RevenueCat shines. Offering a streamlined solution for in-app subscriptions and purchases, particularly for platforms like React Native, it’s becoming the go-to […]
React native Experts